Yesterday we discovered the real way to steal data from a popular password manager LastPass. We recommend that you read this article, so as not to fall for the bait.
We use a variety of online services and Web applications, each of which is necessary for safety reasons to have different user names and passwords. Keeping them all in your head is not possible, so the common use of password managers sets in. They provide secure storage and convenient use of usernames and passwords not only to online services, but also to the payment systems, bank accounts and so on. Therefore, leakage or hacking of the password manager could be a big problem for many users, because its like giving a criminal the key to your bank vault.
One of the most popular applications of this kind is LastPass. It is really an excellent solution that has passed the test of time, and survived the threats of many hackers. Yesterday, however, a computer security expert Sean Cassidy (Sean Cassidy) has found a way for phishing attacks on LastPass. He called this hacking method LostPass (lost passwords).
How is LastPass Hacked?
Firstly, we need to talk about how these hackers lay their hands on your LastPass credentials. The new LastPass Hacking method seems straightforward and easy even for beginners. We would not talk much about the attack itself as that can be gotten from here.
The vulnerabilities found is as follows;
First, the attacker entices you to their website, which shows a fake (!), A notice that your session has expired and you must login again. You’ve probably seen these notifications by LastPass.
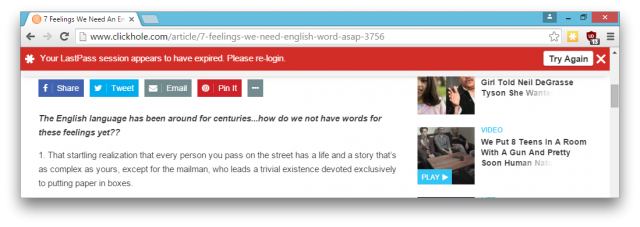
Since the notification is fake, clicking the Try Again button will take you to a specially designed page that looks just like a standard form for entering login and password on LastPass. Even the address will be almost the same, which usually have special pages browser, unlockable installed extensions. Except for the small detail that I’ve highlighted in the screenshot below. I am sure that most people do not pay attention to such details.

Leave a Reply
You must be logged in to post a comment.